Government
Standardised control, documented at every step.
Public sector estates carry an obligation to demonstrate consistent configuration and controlled administration across agencies and locations. AegisOne provides the inventory and the audit record to support it.
The problem
What we hear from teams in this sector
None of this is exotic. It is the ordinary consequence of an estate that grew faster than the systems keeping track of it.
Auditability above all
Every administrative action must be attributable and retained.
Distributed agencies
Multiple sites with differing local capability and connectivity.
Data residency
Where data is processed and stored is a procurement requirement, not a detail.
Standardised reporting
Oversight bodies expect a consistent format across reporting periods.
Unassessed is its own category
Illustrative example, not research or customer data. It illustrates a distinction the platform preserves: a device that has not been assessed is reported separately rather than counted as conformant.
What applies
7 AegisOne capabilities relevant to Government
Every capability below is running in production and available in the demo environment. This list is generated from the product registry, so it can never include something we have not built.
Asset Intelligence
Hardware and software inventory with a full lifecycle timeline for every asset.
Compliance Frameworks & Evidence
Score endpoints against control frameworks and export the evidence auditors request.
Vulnerability & Risk Register
Track vulnerabilities, security findings, incidents and business risks together.
Patch Management
Scan, install and roll back patches on managed endpoints.
MFA & Audit Logging
Multi-factor authentication for operators and a durable audit trail.
Network Discovery
Scan a network range and surface devices that have no agent on them.
Executive Reporting & Export
Board-ready reporting exported to PDF, Excel and PowerPoint.
What this looks like in the console
An illustration of the part of the console this sector spends the most time in. The layout is the product; the values are invented for the example.
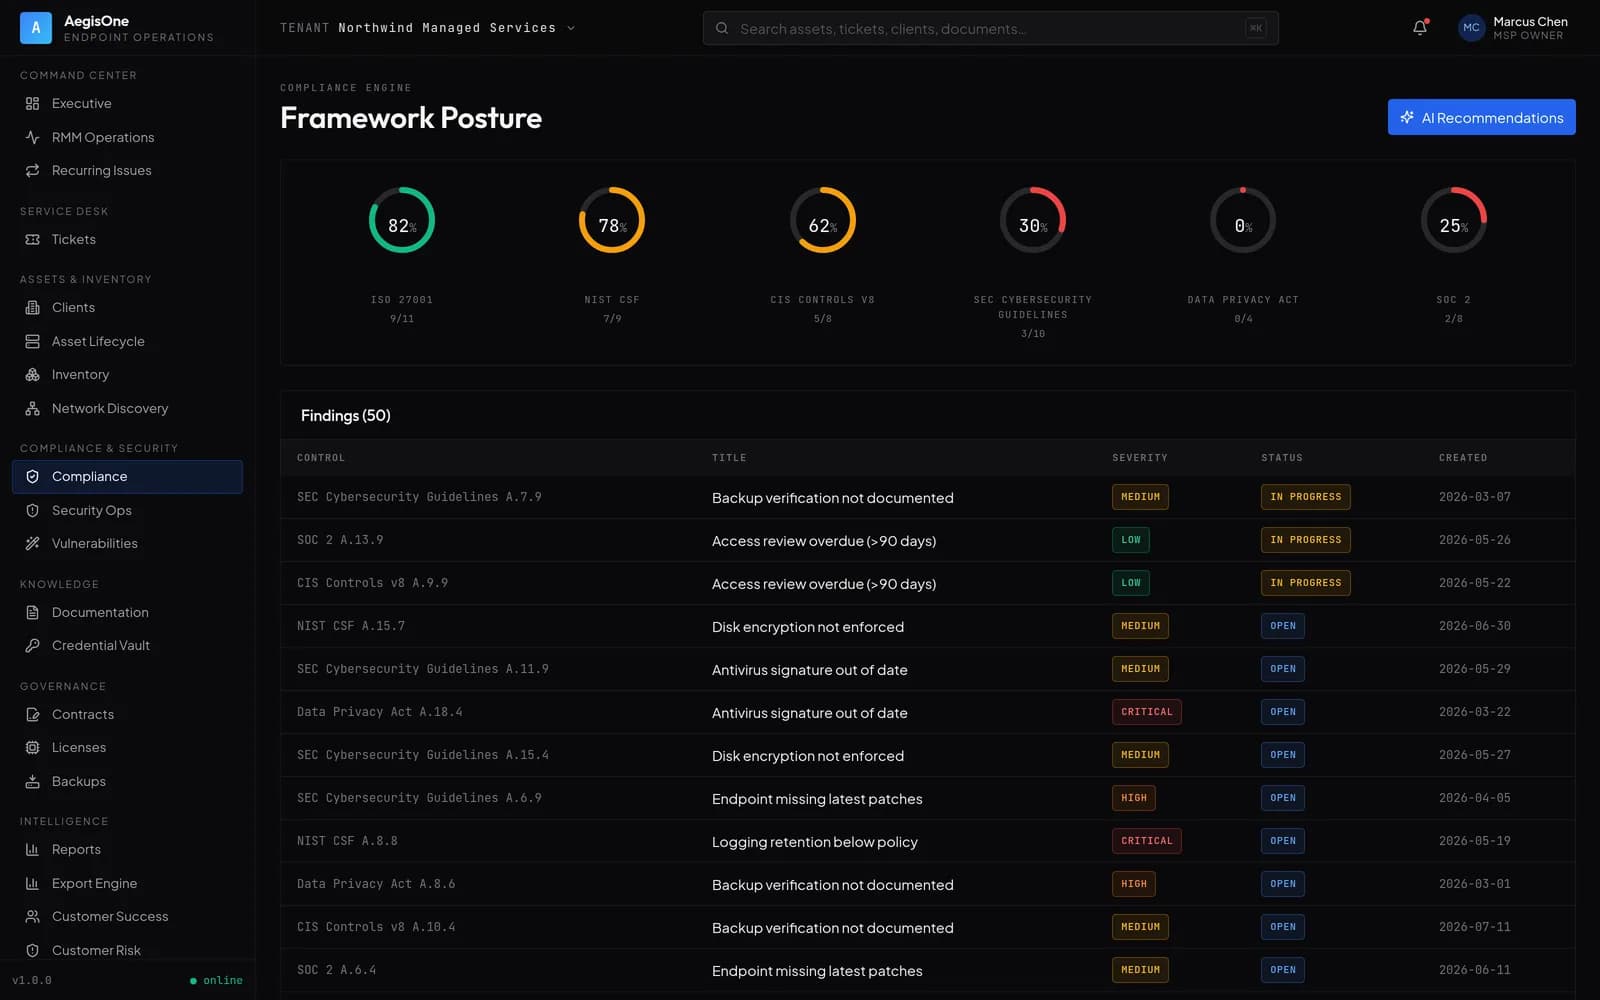
Only shipped capabilities appear on this page. If you were expecting something that is missing, it is likely on the public roadmap rather than absent from our thinking.
Example workflow
How the platform is typically operated here
A four-step rhythm rather than a project. Each step produces the input the next one needs, which is what keeps the reporting current instead of assembled the week before it is due.
- 01
Baseline
Establish a verified inventory across every agency site.
- 02
Harden
Track configuration and patch position against the standard.
- 03
Attribute
Bind every administrative action to a named operator.
- 04
Report
Produce consistent reporting for oversight and audit.
Security considerations
Controls that matter in this environment
A platform with administrative reach into every endpoint is itself part of your attack surface. These are the controls AegisOne applies to its own operation.
- Named-operator attribution on every privileged action
- Multi-factor authentication enforced for administrative access
- Deployment location is a configurable commitment — ask us about residency
Recommended reports
What to put in front of stakeholders
These are the reports teams in this sector generate most often. Each exports to PDF, Excel or PowerPoint from the report catalogue.
Agency estate inventory
Configuration and patch conformance
Administrative action audit
Vulnerability exposure by site
Compliance considerations
Frameworks that usually apply here
Read the claim level on each one carefully. It describes precisely what AegisOne does and does not assert — the difference between our controls being designed against a standard and our platform helping you evidence your own obligations under it.
ISO/IEC 27001
CompliantAegisOne is ISO/IEC 27001 compliant. Our information security management controls are implemented in line with the standard, covering access control, asset management, operations security, audit logging and vulnerability management.
NIST Cybersecurity Framework
Designed to supportAegisOne capabilities map to Identify, Protect, Detect and Respond functions of the NIST Cybersecurity Framework.
CIS Controls
Designed to supportAegisOne supports implementation of foundational CIS Controls, particularly inventory, vulnerability management and controlled administrative access.
AegisOne supports your compliance programme; it does not make your organisation compliant, and no statement on this site should be read as a certification we hold on your behalf. Full claim definitions are published on the compliance page.
See this against your own estate
Start a demo pre-loaded with a realistic managed estate, or have someone walk through the government workflow against your actual environment.