Security & Compliance
Vulnerability & Risk Register
Track vulnerabilities, security findings, incidents and business risks together.
Status: Available · Specified in FRD §19
What it is
Available today
Security findings, vulnerabilities, incidents and risk records live in one register so the technical detail and the business exposure can be reported side by side.
This sits within security & compliance — harden endpoints and produce the evidence auditors ask for. It is part of the same platform as every other capability listed on this site, which means the data it produces is available to reporting, compliance evidence and the audit trail without an export step in between.
What you get
- Vulnerability register with per-endpoint linkage
- Security findings and incident records
- Business risk register
- Feeds the executive and board reporting layer
- Capability group
- Security & Compliance
- Status
- Available
- Specification reference
- FRD §19
The specification reference points at the section of our functional requirements document that defines this capability, so that what is written here can be traced back to what was actually specified and built.
In the console
What vulnerability & risk register looks like in use
An illustration of the interface for this capability. The layout is the product; the values in it are invented for the example, which is why the frame says so.
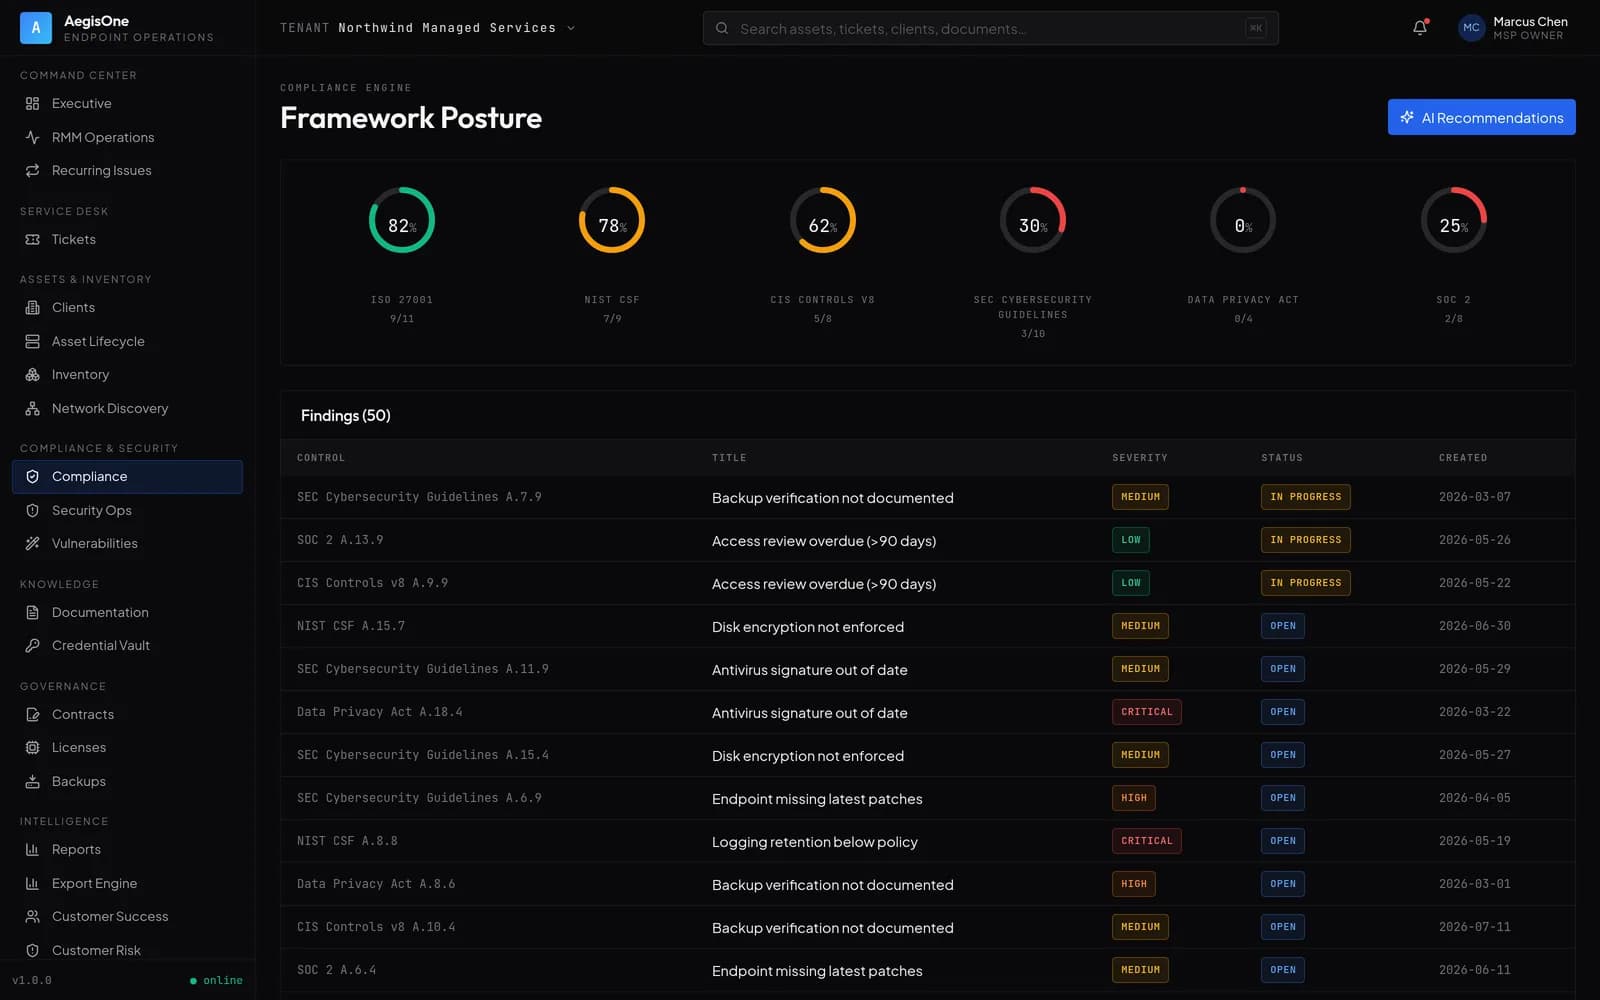
Security & Compliance
Related capabilities
Other things AegisOne ships in this area. Harden endpoints and produce the evidence auditors ask for.
Compliance Frameworks & Evidence
Score endpoints against control frameworks and export the evidence auditors request.
Read moreCredential Vault
Store client credentials with controlled, audited reveal.
Read moreMFA & Audit Logging
Multi-factor authentication for operators and a durable audit trail.
Read moreSee vulnerability & risk register against a real estate
The 14-day demo environment comes pre-loaded with a realistic fictional managed estate, so you can exercise this capability with data in it rather than an empty console. No credit card required.